Your Staff Already Use AI. Here Is How We Keep Your Data Out of It.
Employees at small and mid-sized firms are pasting client files, patient details and code into AI chatbots every day, and most owners cannot see it. Southeastern Technical now runs AI governance and control as a managed service: see every AI tool in use, strip sensitive data out of prompts in real time, and prove it to auditors.
Ask a business owner whether their staff use AI at work and the usual answer is “a little, probably.” Ask what data has gone into it and the answer is a pause.
That pause is the problem. Two years ago, using AI at work meant asking a chatbot to polish a job description or tidy an email. Today it means an HR coordinator uploading a folder of employee files to get a pay analysis, a salesperson pasting the whole customer list into a third-party tool to plan renewals, and a developer letting a coding assistant read the entire codebase. None of that is malicious. All of it moves company data to services the business does not control, and in most offices nobody can see it happening.
We have been asked about this enough times that we now run AI governance and control as a managed service. This post explains what that means in practice, why “just block it” does not work, and what you get.
The four ways AI exposure shows up
The same pattern appears in every department, and it always starts with good intentions.
- HR and people. Then: rewriting a performance review template. Now: employee records with pay and health details uploaded for analysis. Result: no policy, no audit trail, personal data exposed.
- Engineering and technical staff. Then: autocomplete on a few lines of code, reviewed by a person. Now: AI agents with access to the full codebase that open changes and call other systems. Result: intellectual property and credentials leaking out, with no visibility.
- Sales and client service. Then: rephrasing a cold email. Now: the CRM, with revenue figures and renewal dates, pasted into a public AI tool. Result: client data and contract terms shared without consent.
- Leadership. Then: a one-page “approved tools only” policy that nobody enforced. Now: a client, an insurer or the board asks how AI is governed, and nobody can answer with evidence.
For our medical and dental clients the stakes are specific. A patient name and a diagnosis in a chatbot prompt is protected health information leaving the practice. For law firms it is privileged material. For accounting firms in January it is taxpayer IDs and bank numbers. For engineering firms it is the drawings and bid numbers that win the work.
Why blocking AI does not work
The instinctive fix is to block ChatGPT at the firewall and move on. We understand the appeal. It does not work, for three reasons.
First, there are not five AI tools to block, there are thousands, and new ones appear every week inside products your staff already use. Second, people who find AI useful keep using it, on their phones and on personal accounts, where you have no visibility at all. Third, your competitors are using AI to get more done, and a blanket ban gives that away.
So the goal is not to stop AI. It is to let your staff use it while you decide what data it gets to see.
What AI governance and control actually does
Here is what changes once the service is in place. Each of these is running today, not a roadmap item.
You see every AI tool in use. Within days you have an inventory of every AI website, app, copilot and assistant your staff use, sanctioned or not, with who uses it, how often, and how risky each tool is. That includes desktop AI apps, not just the browser, and it shows when someone signs into a personal AI account on a work device.
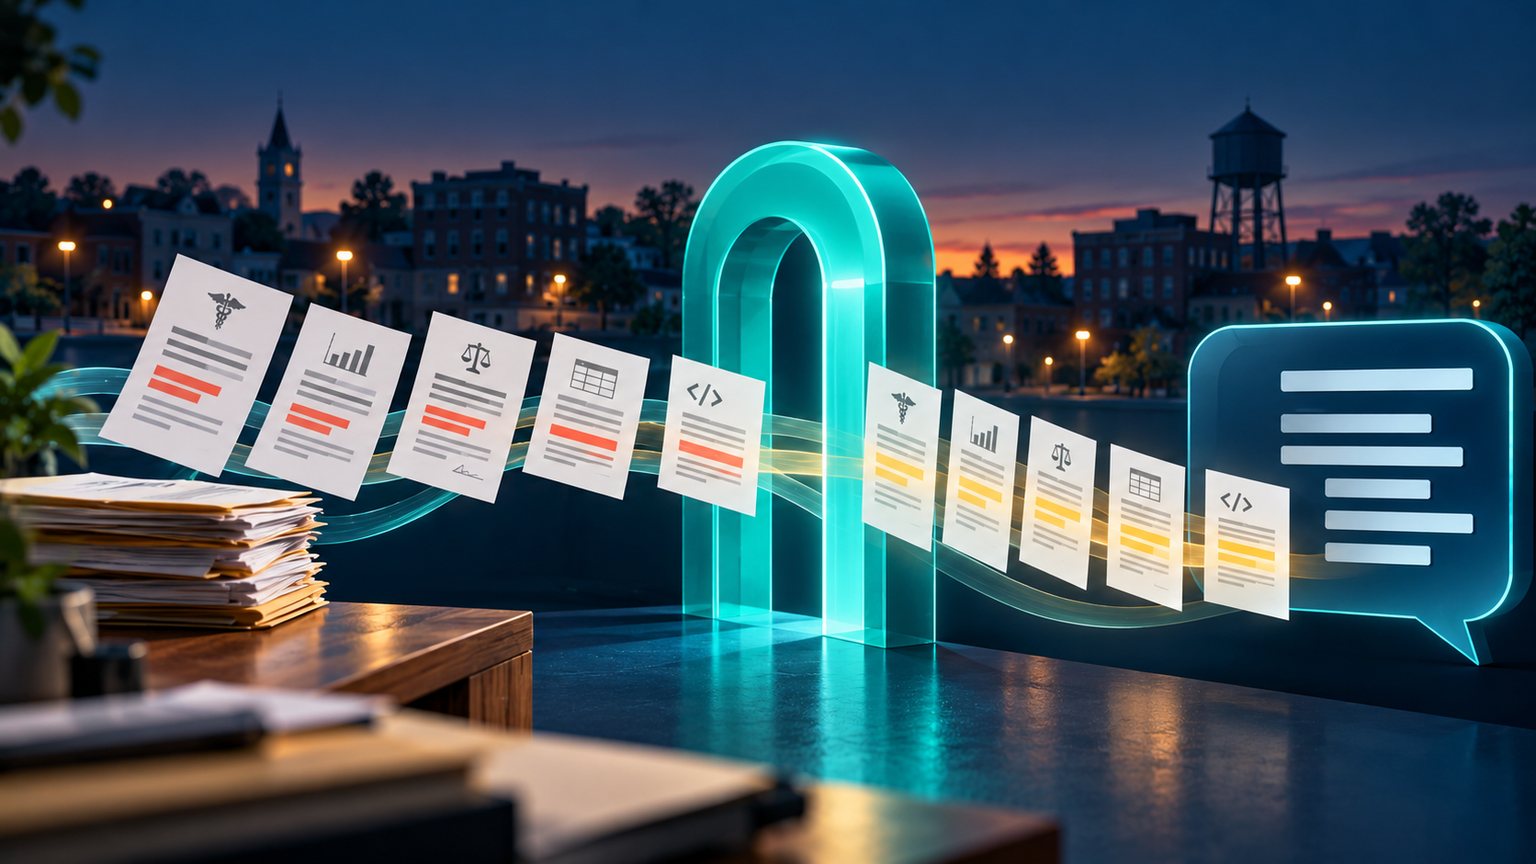
Sensitive data is stripped out before it reaches the AI tool. Every prompt is checked before it reaches the AI tool. When it contains something it should not, such as a Social Security number, a bank account, a patient detail, an API key or a client name you have flagged, the platform can swap that value for a realistic fake one and let the rest of the request through. The employee still gets a useful answer. The real value never reaches the AI tool. For data that must never go anywhere, the prompt is blocked with a short explanation.
Your approved-tools list is actually enforced. You decide which AI tools are approved, for whom, and how. The finance team can have one set of rules and the developers another. Unapproved tools are blocked. Personal AI accounts on work devices can be blocked too, which keeps company work inside the company’s own AI subscription, where the business owns the data.
Staff are coached, not just stopped. When someone is about to share something sensitive, they see a short, branded message: what the risk is, what your policy says and what to do instead. Most people only need to see it once.
You can prove it. Every AI interaction is logged with who, when, which tool, what was found and what action was taken, and the history is kept for a year. When a client security questionnaire, a cyber insurance renewal or a HIPAA risk assessment asks how you govern AI, you answer with a report, not a promise.
How we roll it out without disrupting your office
We start in watch-only mode. For two to four weeks the protection is deployed but blocks nothing. It records which tools are in use and what kinds of data go into them. That gives us real evidence to build rules from, instead of guesses, and it means nobody’s day is disrupted while we learn.
Then we sit down with you, walk through what we found and agree the first set of rules: which tools to approve, which to block, which data to redact and which teams need exceptions. Before anything is enforced, we test each rule against sample text so we know exactly what your staff will see.
Enforcement then goes live team by team. After that it is ordinary managed IT: rule changes, new tools and new hires go through the help desk, and you get a monthly report on AI use, what was caught and what we recommend next.
Deployment runs through the device management you already have, on Windows and Mac, and alongside your current antivirus or endpoint security.
The policy and the controls have to match
Many firms already have an AI policy. It usually lives in a shared drive, says “use approved tools only”, and is not enforced. We write or update the written AI acceptable use policy and then make the technical rules match it, line for line, so the policy you show an auditor is the policy that is actually running.
For regulated clients we map those rules to the obligations that apply to you: HIPAA for medical and dental practices, client confidentiality for law firms, taxpayer data duties for accounting firms, and contract and IP terms for engineering firms.
Where to start
The first step is seeing what is already happening. Our 30-day AI exposure assessment deploys in watch-only mode, changes nothing about how your staff work, and ends with a plain-English report on which AI tools your people use, which teams use them and what kinds of data went in, plus the rules we recommend.
Read more about the service on our AI governance and control page, or schedule a free assessment and we will start with what your office is actually doing today.
Frequently asked questions
Why not just block ChatGPT and other AI tools?
Because staff keep using them, on their phones and personal accounts, where the business has no visibility and no control at all. Blocking moves the risk somewhere you cannot see. Governing AI keeps the productivity and keeps the data in your hands: approved tools stay open, unapproved ones are blocked, and sensitive values are stripped out of prompts before they reach the AI tool.
Will this slow my people down?
Usually not noticeably. Most violations are handled by swapping the sensitive value for a realistic stand-in, so the employee still gets a useful answer. Only the data that must never leave is blocked outright, and when that happens the employee sees a short explanation of why and what to do instead.
Can you see what my employees type into AI tools?
The audit trail records each AI interaction, which is what lets you prove governance to an auditor or reconstruct an incident. Because those records can include the sensitive values someone tried to share, access to them is limited to a very small group and reviewed regularly. We manage that access as part of the service.
Does this work if we already have antivirus or another security product?
Yes. The protection runs alongside your existing endpoint security, on Windows and Mac, through the device management you already use. Nothing has to be ripped out.
We are a small medical practice. Is this overkill?
It is sized for small offices. A front desk that pastes a patient note into a free chatbot to tidy up a letter has created a HIPAA problem, whatever the size of the practice. Governance gives you a record that it did not happen, or a precise account of what did, which is what you need for your risk analysis either way.
How do we get started?
With a 30-day AI exposure assessment. We deploy in watch-only mode, change nothing about how your staff work, and come back with a report: which AI tools are in use, by which teams, and what kinds of data went into them. Then we recommend the rules.
Your Staff Already Use AI. Here Is How We Keep Your Data Out of It.
Employees at small and mid-sized firms are pasting client files, patient details and code into AI chatbots every day, and most owners cannot see it. Southeastern Technical now runs AI governance and control as a managed service: see every AI tool in use, strip sensitive data out of prompts in real time, and prove it to auditors.
Ask a business owner whether their staff use AI at work and the usual answer is “a little, probably.” Ask what data has gone into it and the answer is a pause.
That pause is the problem. Two years ago, using AI at work meant asking a chatbot to polish a job description or tidy an email. Today it means an HR coordinator uploading a folder of employee files to get a pay analysis, a salesperson pasting the whole customer list into a third-party tool to plan renewals, and a developer letting a coding assistant read the entire codebase. None of that is malicious. All of it moves company data to services the business does not control, and in most offices nobody can see it happening.
We have been asked about this enough times that we now run AI governance and control as a managed service. This post explains what that means in practice, why “just block it” does not work, and what you get.
The four ways AI exposure shows up
The same pattern appears in every department, and it always starts with good intentions.
- HR and people. Then: rewriting a performance review template. Now: employee records with pay and health details uploaded for analysis. Result: no policy, no audit trail, personal data exposed.
- Engineering and technical staff. Then: autocomplete on a few lines of code, reviewed by a person. Now: AI agents with access to the full codebase that open changes and call other systems. Result: intellectual property and credentials leaking out, with no visibility.
- Sales and client service. Then: rephrasing a cold email. Now: the CRM, with revenue figures and renewal dates, pasted into a public AI tool. Result: client data and contract terms shared without consent.
- Leadership. Then: a one-page “approved tools only” policy that nobody enforced. Now: a client, an insurer or the board asks how AI is governed, and nobody can answer with evidence.
For our medical and dental clients the stakes are specific. A patient name and a diagnosis in a chatbot prompt is protected health information leaving the practice. For law firms it is privileged material. For accounting firms in January it is taxpayer IDs and bank numbers. For engineering firms it is the drawings and bid numbers that win the work.
Why blocking AI does not work
The instinctive fix is to block ChatGPT at the firewall and move on. We understand the appeal. It does not work, for three reasons.
First, there are not five AI tools to block, there are thousands, and new ones appear every week inside products your staff already use. Second, people who find AI useful keep using it, on their phones and on personal accounts, where you have no visibility at all. Third, your competitors are using AI to get more done, and a blanket ban gives that away.
So the goal is not to stop AI. It is to let your staff use it while you decide what data it gets to see.
What AI governance and control actually does
Here is what changes once the service is in place. Each of these is running today, not a roadmap item.
You see every AI tool in use. Within days you have an inventory of every AI website, app, copilot and assistant your staff use, sanctioned or not, with who uses it, how often, and how risky each tool is. That includes desktop AI apps, not just the browser, and it shows when someone signs into a personal AI account on a work device.
Sensitive data is stripped out before it reaches the AI tool. Every prompt is checked before it reaches the AI tool. When it contains something it should not, such as a Social Security number, a bank account, a patient detail, an API key or a client name you have flagged, the platform can swap that value for a realistic fake one and let the rest of the request through. The employee still gets a useful answer. The real value never reaches the AI tool. For data that must never go anywhere, the prompt is blocked with a short explanation.
Your approved-tools list is actually enforced. You decide which AI tools are approved, for whom, and how. The finance team can have one set of rules and the developers another. Unapproved tools are blocked. Personal AI accounts on work devices can be blocked too, which keeps company work inside the company’s own AI subscription, where the business owns the data.
Staff are coached, not just stopped. When someone is about to share something sensitive, they see a short, branded message: what the risk is, what your policy says and what to do instead. Most people only need to see it once.
You can prove it. Every AI interaction is logged with who, when, which tool, what was found and what action was taken, and the history is kept for a year. When a client security questionnaire, a cyber insurance renewal or a HIPAA risk assessment asks how you govern AI, you answer with a report, not a promise.
How we roll it out without disrupting your office
We start in watch-only mode. For two to four weeks the protection is deployed but blocks nothing. It records which tools are in use and what kinds of data go into them. That gives us real evidence to build rules from, instead of guesses, and it means nobody’s day is disrupted while we learn.
Then we sit down with you, walk through what we found and agree the first set of rules: which tools to approve, which to block, which data to redact and which teams need exceptions. Before anything is enforced, we test each rule against sample text so we know exactly what your staff will see.
Enforcement then goes live team by team. After that it is ordinary managed IT: rule changes, new tools and new hires go through the help desk, and you get a monthly report on AI use, what was caught and what we recommend next.
Deployment runs through the device management you already have, on Windows and Mac, and alongside your current antivirus or endpoint security.
The policy and the controls have to match
Many firms already have an AI policy. It usually lives in a shared drive, says “use approved tools only”, and is not enforced. We write or update the written AI acceptable use policy and then make the technical rules match it, line for line, so the policy you show an auditor is the policy that is actually running.
For regulated clients we map those rules to the obligations that apply to you: HIPAA for medical and dental practices, client confidentiality for law firms, taxpayer data duties for accounting firms, and contract and IP terms for engineering firms.
Where to start
The first step is seeing what is already happening. Our 30-day AI exposure assessment deploys in watch-only mode, changes nothing about how your staff work, and ends with a plain-English report on which AI tools your people use, which teams use them and what kinds of data went in, plus the rules we recommend.
Read more about the service on our AI governance and control page, or schedule a free assessment and we will start with what your office is actually doing today.
Frequently asked questions
Why not just block ChatGPT and other AI tools?
Because staff keep using them, on their phones and personal accounts, where the business has no visibility and no control at all. Blocking moves the risk somewhere you cannot see. Governing AI keeps the productivity and keeps the data in your hands: approved tools stay open, unapproved ones are blocked, and sensitive values are stripped out of prompts before they reach the AI tool.
Will this slow my people down?
Usually not noticeably. Most violations are handled by swapping the sensitive value for a realistic stand-in, so the employee still gets a useful answer. Only the data that must never leave is blocked outright, and when that happens the employee sees a short explanation of why and what to do instead.
Can you see what my employees type into AI tools?
The audit trail records each AI interaction, which is what lets you prove governance to an auditor or reconstruct an incident. Because those records can include the sensitive values someone tried to share, access to them is limited to a very small group and reviewed regularly. We manage that access as part of the service.
Does this work if we already have antivirus or another security product?
Yes. The protection runs alongside your existing endpoint security, on Windows and Mac, through the device management you already use. Nothing has to be ripped out.
We are a small medical practice. Is this overkill?
It is sized for small offices. A front desk that pastes a patient note into a free chatbot to tidy up a letter has created a HIPAA problem, whatever the size of the practice. Governance gives you a record that it did not happen, or a precise account of what did, which is what you need for your risk analysis either way.
How do we get started?
With a 30-day AI exposure assessment. We deploy in watch-only mode, change nothing about how your staff work, and come back with a report: which AI tools are in use, by which teams, and what kinds of data went into them. Then we recommend the rules.
Talk to Us About Your Practice
Tell us where your compliance or IT situation stands and we will get back to you. No obligation, and no sales sequence.