AI · Managed Governance & Control
Your Staff Already Use AI. Now You Can See It, And Control It.
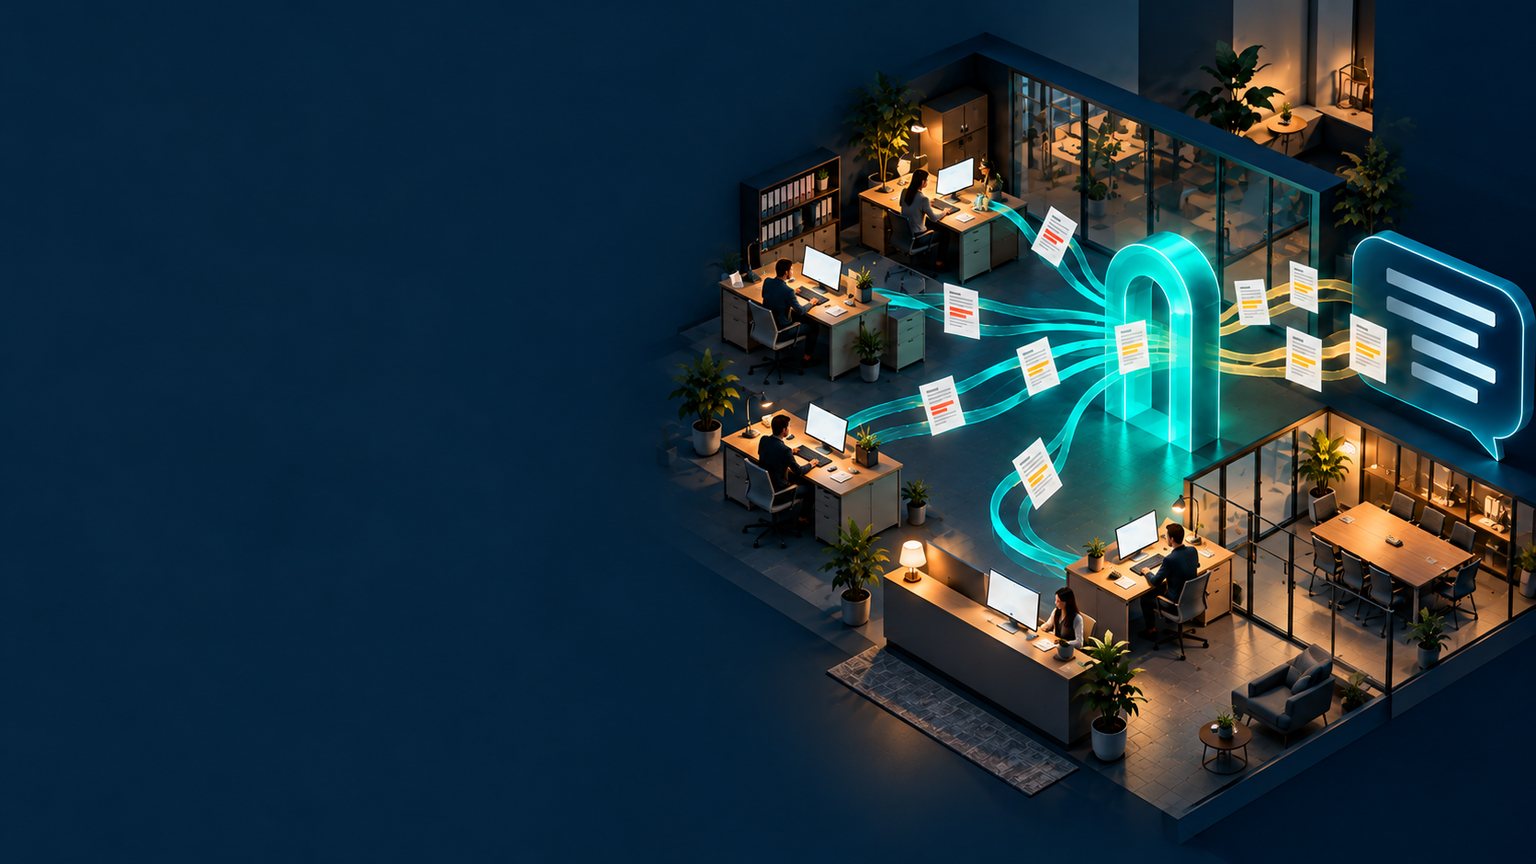
We show you every AI tool your people use, strip client, patient and financial data out of prompts before it reaches the AI tool, enforce your approved-tools list and keep an audit trail you can hand to an auditor, an insurer or your board. Your staff keep the productivity. You keep the data.
AI Use Grew Faster Than Anyone's Rules
The same pattern shows up in every department. Nobody meant any harm, and nobody can see it.
HR & People
Then: Polish a job description.
Now: Employee files with pay and health details uploaded for "analysis".
No policy, no audit trail, personal data exposed
Engineering
Then: Autocomplete a few lines, reviewed by a person.
Now: Coding agents with full codebase access change code and call other systems.
IP and credentials leak, no visibility
Sales & Client Service
Then: Rephrase a cold email.
Now: The CRM, revenue and renewal dates pasted into a public AI tool.
Client data shared without consent
Leadership
Then: A one-page "approved tools only" policy nobody enforces.
Now: A client, insurer or board asks for proof of AI governance.
No evidence, audit exposure
Blocking AI does not fix this. There are thousands of AI tools, and people who find them useful move to phones and personal accounts where you see nothing at all. The answer is to govern AI, not ban it.
What AI Governance & Control Does For You
All of this runs today, on your existing Windows and Mac computers, alongside the security software you already have.
See Every AI Tool In Use
- •Shadow AI discovery across thousands of AI sites, apps, copilots and assistants
- •AI app inventory with users, prompts, violations and a risk score per tool
- •Desktop AI apps and local models, not only the browser
- •Personal vs. work AI accounts on company devices
Keep Sensitive Data Out Of AI
- •Every prompt checked before it reaches the AI tool
- •Sensitive values swapped for realistic stand-ins, so the answer still works
- •Personal, financial, health and regulated identifiers detected by framework
- •Hundreds of detectors for API keys, cloud credentials and tokens
- •Your own terms: client names, matter numbers, project code names
- •File upload, download and paste controls
Enforce Your Approved Tools
- •Approve some AI tools, block the rest, firewall-style
- •Different rules per person, team and application
- •Separate rules for the web and desktop versions of a tool
- •Block personal AI accounts on work devices
- •Private browsing and unmanaged browsers detected
Keep AI On-Policy
- •Block or monitor whole topics, however they are worded
- •Harmful and harassing content moderation
- •Plain-English guardrails such as "no questions about pending litigation"
- •Prompt injection attempts flagged
Coach Staff In The Moment
- •A short message at the moment of risk: why, what policy says, what to do
- •Clear explanation when a tool is not approved
- •Branded with your logo and a link to your AI policy
Prove It To Anyone Who Asks
- •Every AI interaction logged: who, when, which tool, what was found, what happened
- •A full year of history
- •Leadership dashboard and exportable reports
- •Evidence for cyber insurance, client questionnaires and HIPAA risk assessments
Protection That Does Not Stop The Work
Most of the time a prompt is not blocked. The sensitive parts are replaced, and the rest goes through.
What the employee typed
Draft a letter to [email protected] about the refund to account 4401 9928 3310.
What the AI tool received
Draft a letter to [email protected] about the refund to account 7720 1045 8836.
Illustrative example. The employee still gets a useful draft; the real email address and account number never reach the AI tool.
Developers Keep Their AI Coding Assistants
Technical staff get their own rules. AI coding assistants and AI-powered editors stay available, while source code, API keys, cloud credentials and tokens are redacted or blocked before they reach the assistant.
How We Roll It Out
Evidence first, rules second, and nobody's day disrupted along the way.
-
1
Watch
We deploy in watch-only mode for two to four weeks. Nothing is blocked; we record which AI tools are used and what kinds of data go in.
-
2
Report
You get a plain-English exposure report: tools, teams, data types and risk, with the rules we recommend.
-
3
Test & Enforce
Every rule is tested against sample text first, then switched on team by team so nobody is surprised.
-
4
Run
Rule changes, new tools and new hires go through our help desk. You get a monthly AI governance report.
The Policy And The Controls Finally Match
Software enforces the rules. We write them, map them to your obligations and keep them current.
AI Acceptable Use Policy
Written or updated in plain language, then enforced line for line by the technical rules.
Approved AI Tools Register
Every approved tool with an owner, the data it may touch and a review date.
Compliance Mapping
HIPAA for medical and dental, confidentiality for law, taxpayer data for accounting, contract and IP terms for engineering.
Monthly Governance Report
Usage trends, new shadow AI, what was caught, rule changes and recommendations, walked through with you.
Quarterly Review
A working session on what changed in your AI use, what regulators announced and what we recommend next.
AI Incident Response
If something sensitive does reach an AI tool, we reconstruct what happened from the audit trail, contain it and document it.
Three Ways To Start
30 days, fixed fee
AI Exposure Assessment
Any business that wants to know what is happening today
- ✓Watch-only deployment
- ✓AI tool and data exposure report
- ✓Recommended rules and policy
- ✓Executive walkthrough
Per user, monthly
AI Governance Essentials
Small offices, medical and dental practices, accounting firms
- ✓Discovery, data protection, approved-tools enforcement
- ✓In-the-moment staff coaching, branded
- ✓Audit trail and monthly report
- ✓Managed deployment and help-desk administration
Per user, monthly
AI Governance Plus
Law and engineering firms, multi-site offices, firms with developers
- ✓Everything in Essentials
- ✓AI coding assistant protection for developers
- ✓Policy writing and compliance mapping
- ✓Quarterly reviews, incident response, audit evidence packs
Common Questions
Why not just block ChatGPT and other AI tools?+
Because staff keep using them on phones and personal accounts, where the business has no visibility at all. Blocking moves the risk somewhere you cannot see. Governance keeps approved tools open, blocks unapproved ones and strips sensitive values out of prompts before they reach the AI tool.
Will this slow my staff down?+
Usually not noticeably. Most violations are handled by swapping the sensitive value for a realistic stand-in, so the employee still gets a useful answer. Only data that must never leave is blocked outright, with a short explanation.
Does it work alongside our current antivirus or security software?+
Yes. It runs alongside your existing endpoint security on Windows and Mac and is deployed through the device management you already use.
Who can see what employees type into AI tools?+
The audit trail can include the sensitive values someone tried to share, so access is limited to a very small group and reviewed regularly. We manage that access as part of the service.
Can developers keep using AI coding assistants?+
Yes. Developers get their own rules, and source code, API keys and tokens are redacted or blocked before they reach the assistant.
How do we start?+
With the 30-day AI Exposure Assessment. It changes nothing about how your staff work and ends with a report on which AI tools are in use, by whom and with what data.
From The Blog
Your Staff Already Use AI. Here Is How We Keep Your Data Out of It.
Why blocking AI fails, what governance changes in a real office, and how the rollout works.
AI Risk Area
Oversight & Governance
The wider governance picture: overreliance, decision authority, reliability and explainability.
Find Out What Your Office Is Already Sharing With AI.
The 30-day AI Exposure Assessment changes nothing about how your staff work. It ends with a plain-English report and the rules we recommend.
Schedule Your Free AssessmentOr call us directly: (678) 807-6156
Talk to Us About AI Governance
Tell us how your team uses AI today and what worries you about it, and we will tell you what an assessment would show.